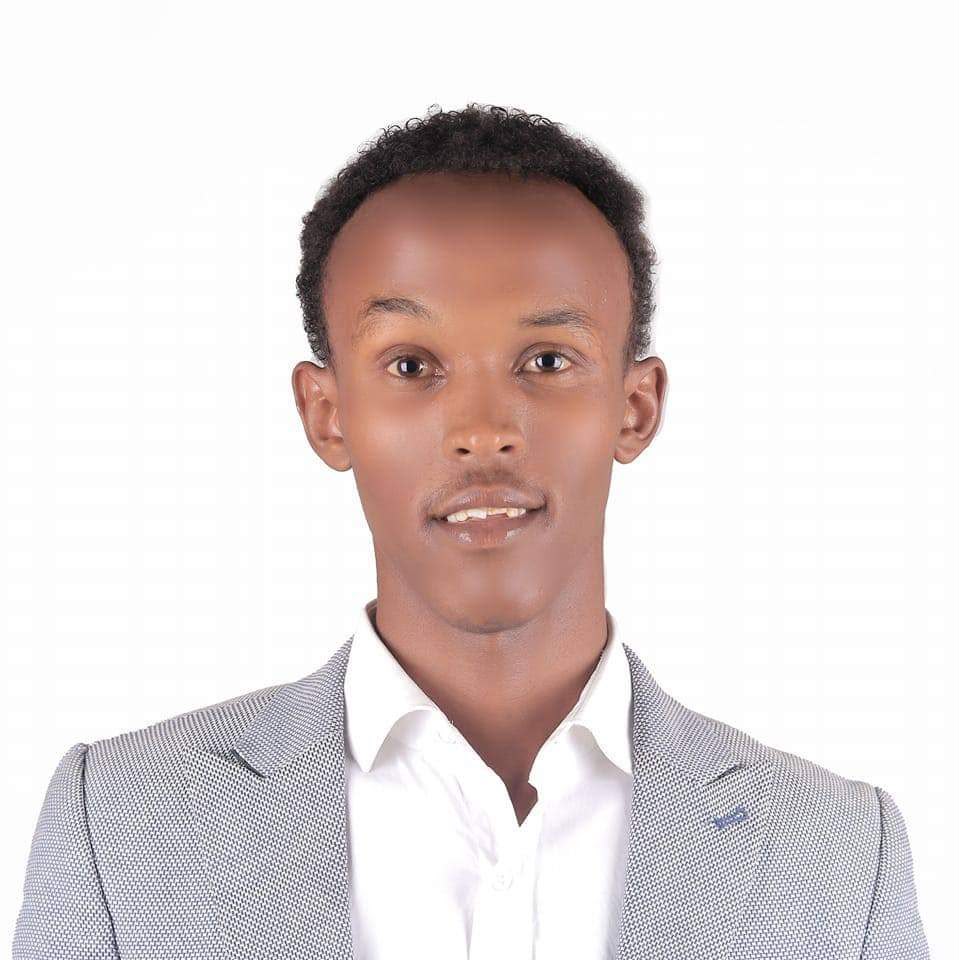
I’m Yusuf Khalid Shire, a Master’s student in the Department of AI Convergence at Kookmin University in Seoul, where I work in MCLab with Professor Sang-Chul Kim. I started there in September 2025.
My work sits where AI security, AI safety, and AI policy meet. The question I keep coming back to is how the defenses we put in front of language models fail, and how to measure that failure honestly instead of reporting one flattering number. My first paper is a benchmark for prompt-injection detectors that measures what they do to legitimate security-related text, not only whether they catch attacks. The part I am increasingly drawn to is what such results should mean beyond the lab: how evaluation evidence like this should shape safety requirements, deployment standards, and the policy written for AI systems. Future papers and projects here will follow that line.
Why this blog exists
Two reasons.
Writing is how I check whether I understand something. If I cannot explain an attack in plain language, with a concrete example and a number I can source, I do not understand it yet.
And when I started, most AI security material was either a research paper (dense, assumes you already know the field) or a social-media thread (loud, often wrong). Short, sourced, reproducible explanations were hard to find. That is the gap I write into.
What you will find here
So far: explanations of attacks and defenses, and write-ups of my own research, with the code behind them. Research posts end with the experiment I would run next, because that is usually the most useful thing in them.
Publications
- Yusuf Khalid Shire and Sang-Chul Kim. PIDS-Bench: Evaluating Prompt-Injection Detectors Under Over-Defense, Obfuscation, and Distribution Shift. IEEE Access, vol. 14, 2026. DOI · arXiv · benchmark and code